

dsh-redteam-model
Manifest valid★ 781Based on the dsh web implementation with multiple modes, the purpose is to serve redteam authorized security research, covering areas such as penetration testing, red team assessments, and code auditing. Please do not use it for illegal activities. (Secondary development is permitted, allowing modules to have their own business logic—a methodology is only effective when you're proficient in it; good methodology equals a good ecosystem)
dsh-redteam-model
It went empty into chit-chat. A concern of a veteran security professional: in an AI environment, knowledge points are many and the knowledge surface is very broad. If you keep feeding knowledge to the AI, it can answer when you ask, but if you ask it to complete a task without specifying how to complete it, how to do it efficiently, and how to hit the points you need—even though it holds a large amount of knowledge, without that "workflow" to guide and control it, you may get the result you want, but it often wastes tokens a lot. And sometimes, without guardrails on certain aspects, it can get stuck in a dead end. This is why we keep designing and refining workflows, turning our own experience into skills or agents, so that it can complete tasks following the workflow + receive auxiliary support from the side, thereby working efficiently.
dsh's design in this area of security work is actually limited; it can only be designed from the playbook. The carrier of the plugin itself is still dp-harness. Why we developed this—maybe just because we were following the trend, and we also hope DeepSeek will become cheaper... (On the other hand, harness's advantages are particularly obvious. Personally, in doing "anti-refusal," harness is really too easy compared to Claude's native hooks, Codex's native hooks, or the account-ban risks caused by other third-party agents.)
In a word, this project may not be as good as everyone thinks, nor as cool as the source-code engines others have built, but it is dedicated to one point, and only one:
————Keep refining the workflow; use the workflow approach to fill in as many gaps as possible; efficiency + authenticity is the core.
Ten redteam security research working modes (presets) and their runtime plugins, implemented on top of dsh web. Self-contained and deployable offline. The goal is to serve redteam for authorized security research, covering penetration testing, red team assessment, code audit, binary analysis, AV evasion & counter-evasion, incident response & forensics, cloud security offense/defense, CTF solving, and asset mapping.
This project is an add-on that empowers https://github.com/deepseek-ai/deepseek-harness. Install deepseek-harness first, then install this project;
Do not use for illegal activities. This project is intended only for authorized security testing, CTF, bug bounties, and security research (see the disclaimer below).
如果各位对插件的方法存在不适用自身的情况,那么可以进行两种更改:
1、源码层,调整各个模式的方法论。
2、在"AttackAtlas"插件中,右上角具备两个功能"自定义工作方法论"&"能力库",如果内置能力中,没有你需要的能力,可以在"能力库"中添加主类、子类,完成以后再到"自定义工作方法论"中构建属于你的工作方法论(类似于workflow),有问题欢迎提或者自己再改。
Ten Working Modes
| 模式 | 定位 |
|---|---|
redteam 安全研究员 | Generalized mode; this mode does not define a forced Gate chain. In general, ordinary tasks can be asked here, but for deep tasks, switch to a specialized mode! (专业模式才是初衷) |
pentest 渗透测试 | Professional-grade pentesting for Web/API/app/mini-programs, etc.; |
code-audit 代码审计 | White-box source audit, dynamic & static code audit |
binary-analysis 二进制分析 | Malware analysis, reverse engineering & cracking, unpacking & restoration |
attack-defense 攻防评估 | Multiple main threads: web probing + internal network environment (the internal network environment is further split into Windows scenarios, Linux scenarios, presence/absence of monitoring, domain environments, cloud internal networks, etc.) |
av-evasion 免杀对抗 | Offense-side AV evasion (can be used for shell/loader/C2 mutation; the core point is how to counter the model's "refusal") |
incident-response 应急溯源 | Windows/Linux emergency response & attack tracing: multi-scenario definitions. It is recommended that the prompt clearly describes which scenario it is in (mining, worms, virus/trojan offense-defense investigation, etc.) — if interested, check out the other project dumpall + AI analysis, it's really handy. |
cloud-security 云安全攻防 | Cloud platform & cloud-native penetration: no need to belabor this here, |
ctf-solver CTF 解题 | CTF competition solving: problem registration, module routing (web/pwn/reverse/crypto/misc, etc.), solving loop, flag ledger & retrospective |
asset-mapping 资产测绘 | Asset mapping: supports FOFA/Hunter/Quake/ZoomEye/Shodan + subdomain/DNS validation + ICP filing attribution + fingerprint identification, producing an auditable asset inventory Excel (six worksheets, see the template) |
Each mode is self-contained with four layers of assets:
1、persona (role / epistemology / boundaries / reporting discipline)
2、playbook (methodology & gate text contract)
3、skills (loadable skills)
4、refs/ (external knowledge base, original documents indexed).
Runtime Plugins
| Plugin | Role |
|---|---|
dsh-stage-gate | stage_gate/gates_list tools: structural validation of the 32 stage gates across the eight modes, verdicts written to gate-log.md; operation_goal/operation_progress goal contract & progress closure (driven by operation-state.json for interruption recovery) |
dsh-route-boost | Per-round governance envelope: phase inference + gate checklist + mode boundaries + evidence-level pre-judgment + refs pointers + skill dependency tool-surface readiness line + operation recovery line, task-caliber decisions, structured marker block injection, line-granularity budget, deliver-only-on-change with injection-volume accounting |
dsh-sec-enforce | Deterministic tool interception: report gate, write boundaries, confirm-before-execute for high-risk commands, bare-scan rate limiting |
dsh-refusal-guard | —————Anti-refusal—————AGENTS.md fallback |
dsh-trace-vault | Process trace vault: tool calls from all ten security-mode sessions stored in full; trace_search/trace_get/trace_recent/trace_stats retrieval & session profiling; |
dsh-auto-advance | Auto-advancer: when a subagent executor returns and the intent ledger has unclosed directions, inject an advance reminder; one-shot reminder for the three opening registrations; three guardrails — round cap / human-takeover reset / cooldown window; zero interference for sessions without a ledger |
dsh-product-subagents | subagent_claude_code/subagent_codex providers: headless spawn of local claude/codex CLI; cross-harness re-verification is triggered by the user per recommendation item |
dsh-mcp-studio | MCP loading workbench: onboarding, status, and diagnostics for generic MCPs (burpsuite/yakit/chrome-dev-mcp, etc.) |
dsh-redteam-results | redteam results: task-ledger war-room dashboard + five-panel results page, cross-session aggregation and time-range filtering across nine modes, SQLite row-level persistence |
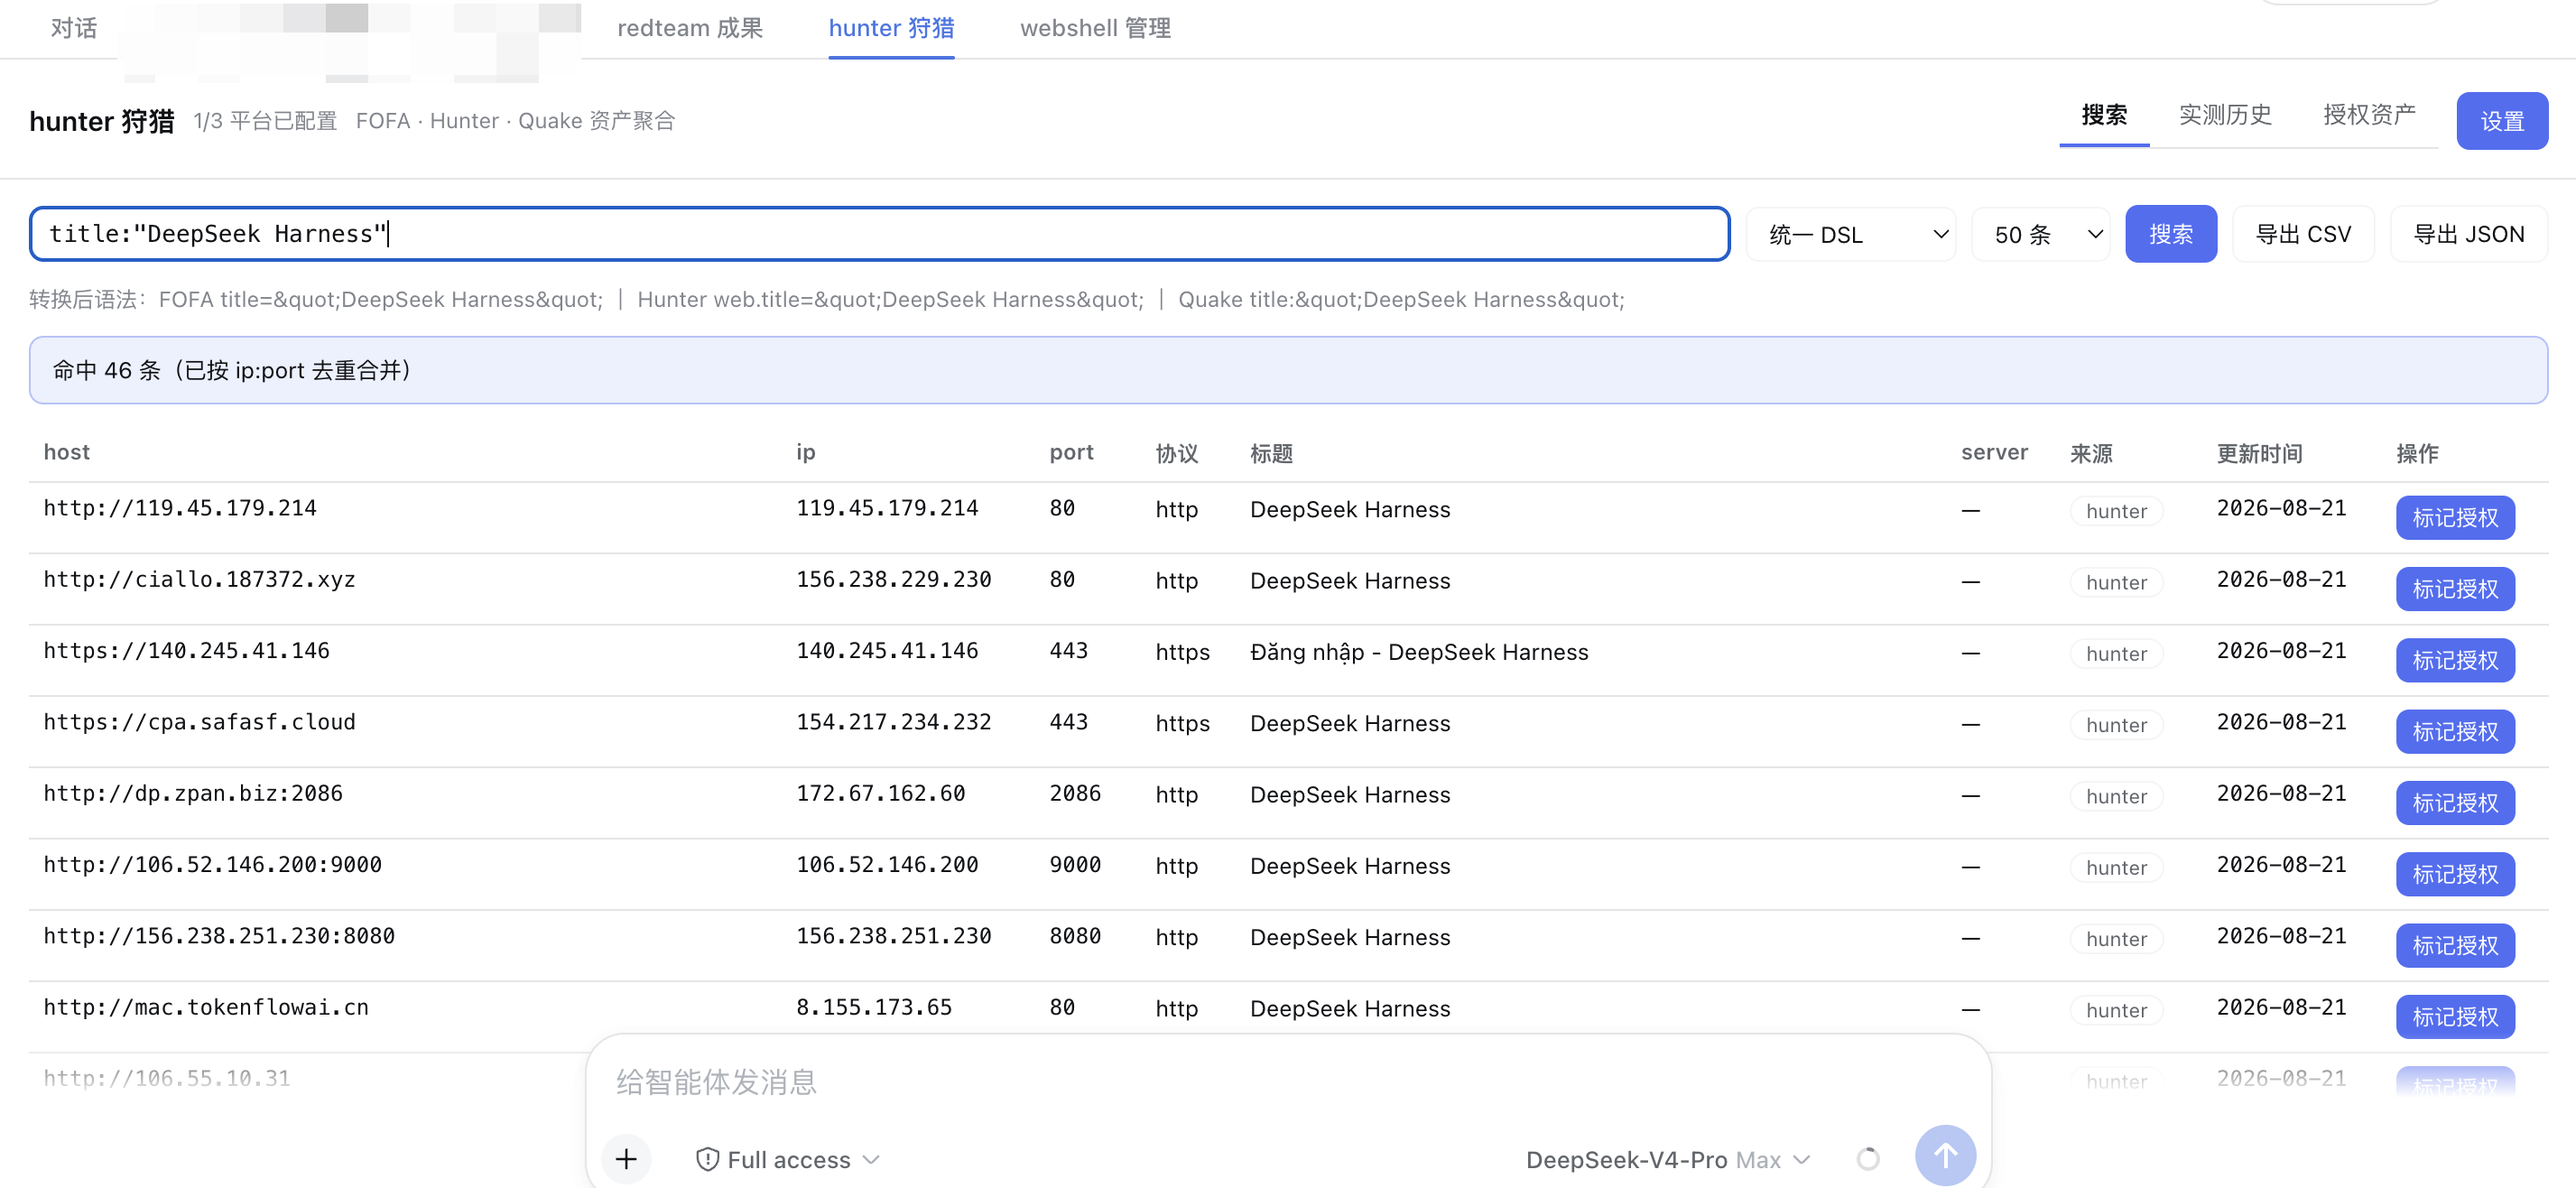
dsh-hunter | hunter hunting: asset search across the FOFA / Hunter / Quake three platforms; one-click verification on the code-audit results page via the "Live Test" button (fingerprint search → liveness probe → EXP verification, executed only on authorized assets) |
dsh-campaign-memory | Campaign memory: cross-session playbooks sediment; same mode + same workspace + same topic writes refresh without duplication; full-text read accounting, heat × 30-day time-decay ranking, recall isolated by workspace; detection fingerprints auto-cleaned after 30 days, target fingerprints expire after 180 days but remain searchable; |
dsh-mode-group | Two-level mode selector on the new-session screen: built-in modes and researcher mode stay at the top level; the nine specialized security modes are folded into the "Specialized Security Modes" hover/click submenu |
dsh-session-pulse | Session status panel (ten modes): top-right task progress chip (live task-list summary done/total + progress bar, turns green when all complete) + subagent chips; right-side "Subagent Directory" drawer (grouped by running/finished, click a name to enter that subagent session and view its running content; the directory updates in real time while open); left-side "Prompts" column on the chat page (user inputs listed in order, hover to preview, click to smoothly locate to the message and highlight it; visible only on the chat tab) |
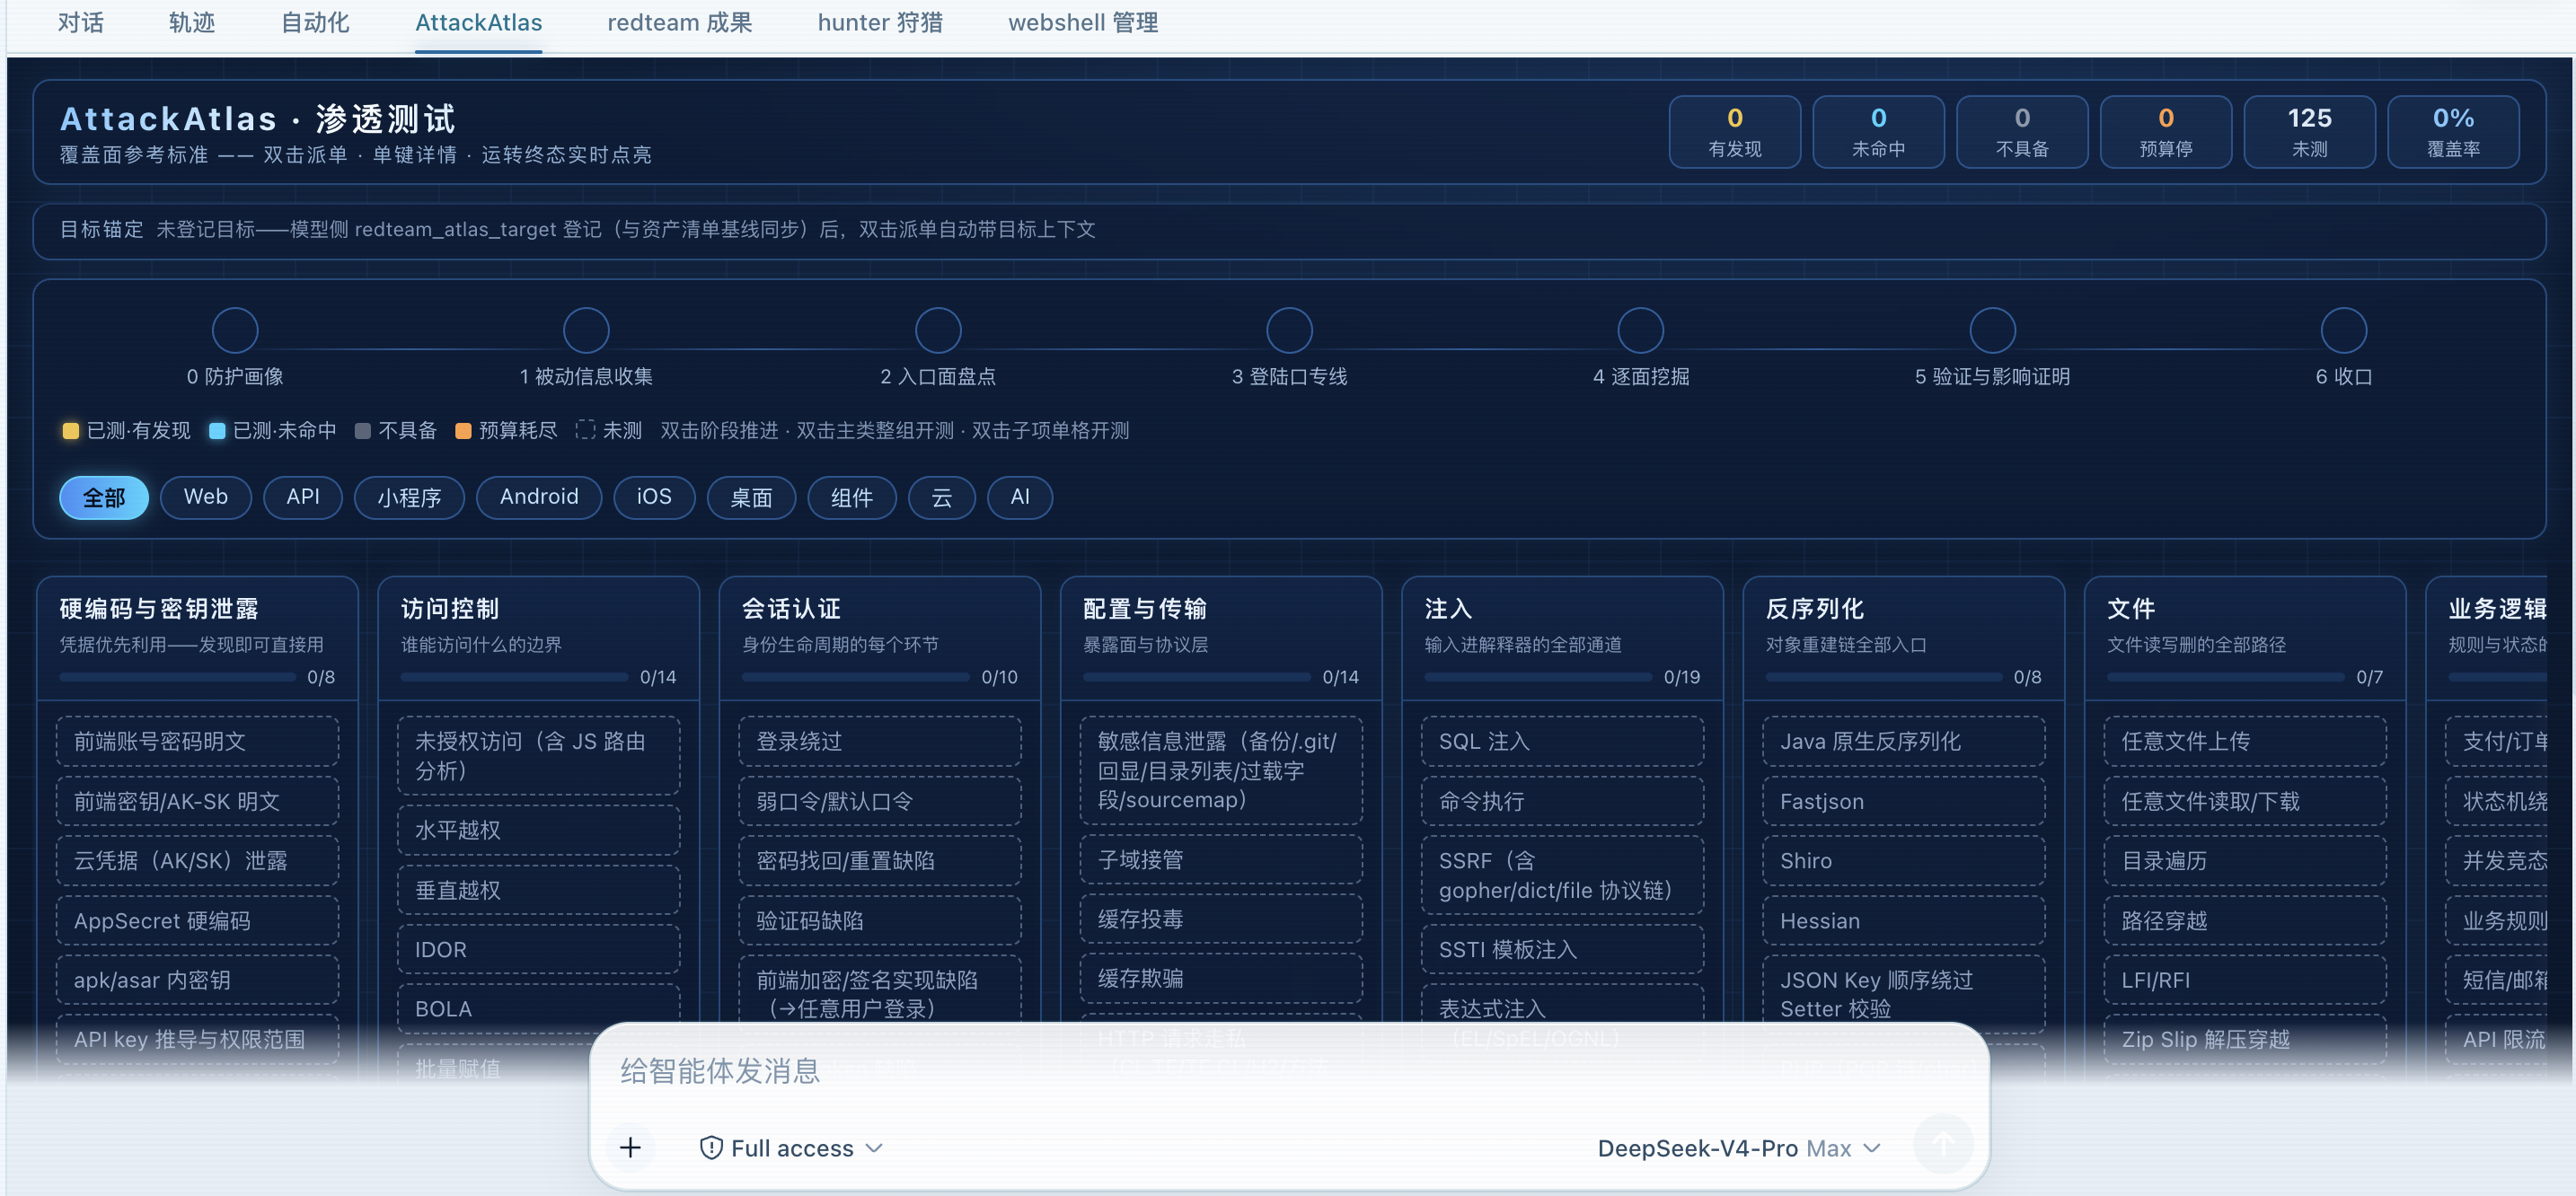
dsh-attack-atlas | AttackAtlas attack-surface map: four-state lighting and phase bands for the eight specialized-mode architecture matrix, target anchoring (coverage states accounted per target, current anchor switching, aggregate view; matrix/phase bands/chain topology are independent per target); double-click to dispatch; custom working methodology; tool / MCP / custom tool modules; capability library (custom top-level/sub-levels merged into the map & methodology) |
dsh-scanner-tools | Local scanner wrappers: nuclei/httpx/ffuf + a declarative registry of thirteen tools (nmap·masscan·subfinder·gau·whatweb·wafw00f·dirsearch·sqlmap·nikto·hydra·impacket·netexec·crackmapexec) — six-node tool-calling ladder (local → MCP → installed alternative → MCP fallback → ask to install → script), conservative defaults + explicit-overrides logged, blind-fire prevention registration, full-text dump to disk + preview cap + circuit breaker on consecutive failures |
dsh-semgrep-audit | semgrep_scan tool: local semgrep wrapper + preset offline rule set auto-location (java self-built / php / oss three tiers); hits are dual-written to scan-reconcile.md/.csv for reconciliation (hit ≠ vulnerability; only promoted after re-verification via chain completion and results registration); detection-only — never auto-installs, --metrics=off offline, artifacts only written to the task workspace |
dsh-webshell-mgr | webshell management: webshell generator → auto protocol-detection connection → command execution / file management / database operations / payload plugin system, operation-ledger audit; offense/defense assessment mode foothold operation-section methodology wiring |
Installation
Prerequisites: Node.js >= 22 (required by DSH itself). No pre-installed pnpm/dsh needed (launched via npx); bash/python are optional.
Method 1: Settings Page Console (Recommended)
Install the entire collection as a single dsh plugin (requires dsh web 0.1.0-rc.6+, verified on 0.1.1-rc.2):
dsh plugin --profile web add github:SeaOf0/dsh-redteam-model
Open the dsh web settings page → Redteam Manager, where you can:
- One-click deploy all ten security modes (empty directory uses a bulk symlink; if a real
.agent-presetsalready exists, the manager writes to its managed real copy); - Install / update / uninstall the seventeen runtime plugins;
- View operation progress and failure reasons; the last 50 records are kept per profile, and pending tasks are marked as interrupted failures on restart.
Mode copy state is refreshed by simply reloading the page; host-plane plugin install / uninstall and the manager's own update require a dsh web restart to take effect.
Plugin dependencies and bundle declarations only modify the current profile; modes live in the global .agent-presets under the current DSH_HOME and are shared by profiles under that DSH home. A backup of the declarations is taken before writing to a profile, and on install failure package.json and the lockfile are restored; uninstalling a sub-plugin only removes runtime-state declarations and does not delete source code.
Method 2: Source One-Click Deploy CLI
Obtain the source code via either: git clone https://github.com/SeaOf0/dsh-redteam-model.git, or the repository page Code → Download ZIP and extract.
cd dsh-redteam-model/deploy
node deploy.mjs            # 安装:预设链接 + 插件挂载 + 依赖安装(幂等可重跑)
node deploy.mjs --check    # 离线校验:十预设挂载 + 插件真实 loader 路径 + bundle 声明
node deploy.mjs --start    # 后台启动 dsh web → http://127.0.0.1:3080
npx ./deploy is also supported. Windows (Win10+ ships with bsdtar): the flow is the same; preset symlinks use junctions so no admin is required.
Both install methods write the bundled AGENTS.md as the dsh global file ~/.dsh/AGENTS.md (native dsh mechanism, applies to all sessions, read by new sessions): installs only if the file is absent; if it exists, it is not overwritten and the output explains how to adopt this package's version yourself.
Manual check 2 min after deploy:
- Open http://127.0.0.1:3080, the roster lists ten modes (redteam security researcher + nine specialized modes);
- In any session, have the model call
gates_list; it returns the specialized mode gate schema; - pentest/attack-defense/cloud-security/ctf-solver/asset-mapping sessions can see scan tools like
nuclei_scan(other modes cannot = preset plane is correct); - After initiating a task, a
[route-boost] mode=... phase=...runtime envelope snapshot appears; - Writing to
reports/without passing the report gate will be intercepted by sec-enforce with a redirect.
Machine-specific optional items (missing ones auto-degrade): claude/codex CLI (cross-harness dual-sign channel), nmap/nuclei/httpx/ffuf/jadx/frida/mingw and other toolchains (playbook tool-plane detection + three-tier fallback: detected tool → MCP → install after approval).
Principles & Architecture
Design principle: text discipline (persona/playbook) + runtime enforcement (plugins) — a dual-layer defense — the model cannot self-evaluate gates (structural validation must be a tool call), semantic gates belong to an independent reviewer, key findings require dual sign-off (DSH review + claude/codex review must agree before entering the report), and all verdicts are logged in the audit trail (gate-log/enforce-log/evidence-index).
flowchart TB
    U[用户 @ dsh web :3080] --> PS[模式会话 redteam / pentest / code-audit / binary-analysis / attack-defense / av-evasion / incident-response / cloud-security / ctf-solver / asset-mapping]

    subgraph MODE[模式资产(预设四层)]
        PE[persona 角色与边界]
        PB[playbook 方法论+门禁契约]
        SK[skills 模式技能 + shared 共享技能]
        RF[refs/ 知识库+索引]
    end

    subgraph HOSTPLANE[宿主平面插件(全模式)]
        RB[dsh-route-boost 逐轮治理信封]
        SG[dsh-stage-gate 门禁结构校验]
        SE[dsh-sec-enforce 确定性拦截 guard]
        RG[dsh-refusal-guard 拒答修复]
        SA[dsh-product-subagents 双签 provider]
        MS[dsh-mcp-studio MCP 工作台]
        HU[dsh-hunter 资产狩猎+实测]
        AA[dsh-attack-atlas 攻击面图谱]
    end

    SC[dsh-scanner-tools 扫描工具 preset 平面]

    PS --> PE & PB & SK & RF
    PS -->|每轮装配| RB
    PS -->|工具调用| SG
    PS -->|write/bash| SE
    PS -->|复核委托| SA
    PS -->|审计实测| HU
    PS -->|矩阵覆盖与自定义方法论| AA
    PS -->|pentest/ad 等 5 模式专用| SC
    SG -->|判定| GL[(gate-log.md)]
    SE -->|拒绝留痕| EL[(enforce-log.md)]
    SC -->|产物| EV[(evidence-index.md / scan-reconcile.md)]
Project Structure
dsh-redteam-model/
├── modes/                    # 十个模式预设(DSH 发现器经 ~/.dsh/.agent-presets 链接扫描)
│   └── <mode>/
│       ├── preset.yml        # 模式名与定位
│       ├── agent.cordis.yml  # persona + 组合行(工具/技能/MCP/子代理)
│       ├── skills/           # playbook 等模式技能
│       └── refs/             # 知识库(README.md 全量索引,零本机路径)
├── shared/skills/            # 十预设共享技能(生态协作/独立复核/治理/边界)
├── plugins/                  # 十七个运行时插件(各自含 lib/ 测试/README)
└── deploy/                   # 一键部署 CLI(deploy.mjs / verify-deployment.mjs / check-sources.mjs / DEPLOY.md)
Demo
| Task Console View (data stats display) | Attack/Defense Assessment Mode (data stats display) |
|---|---|
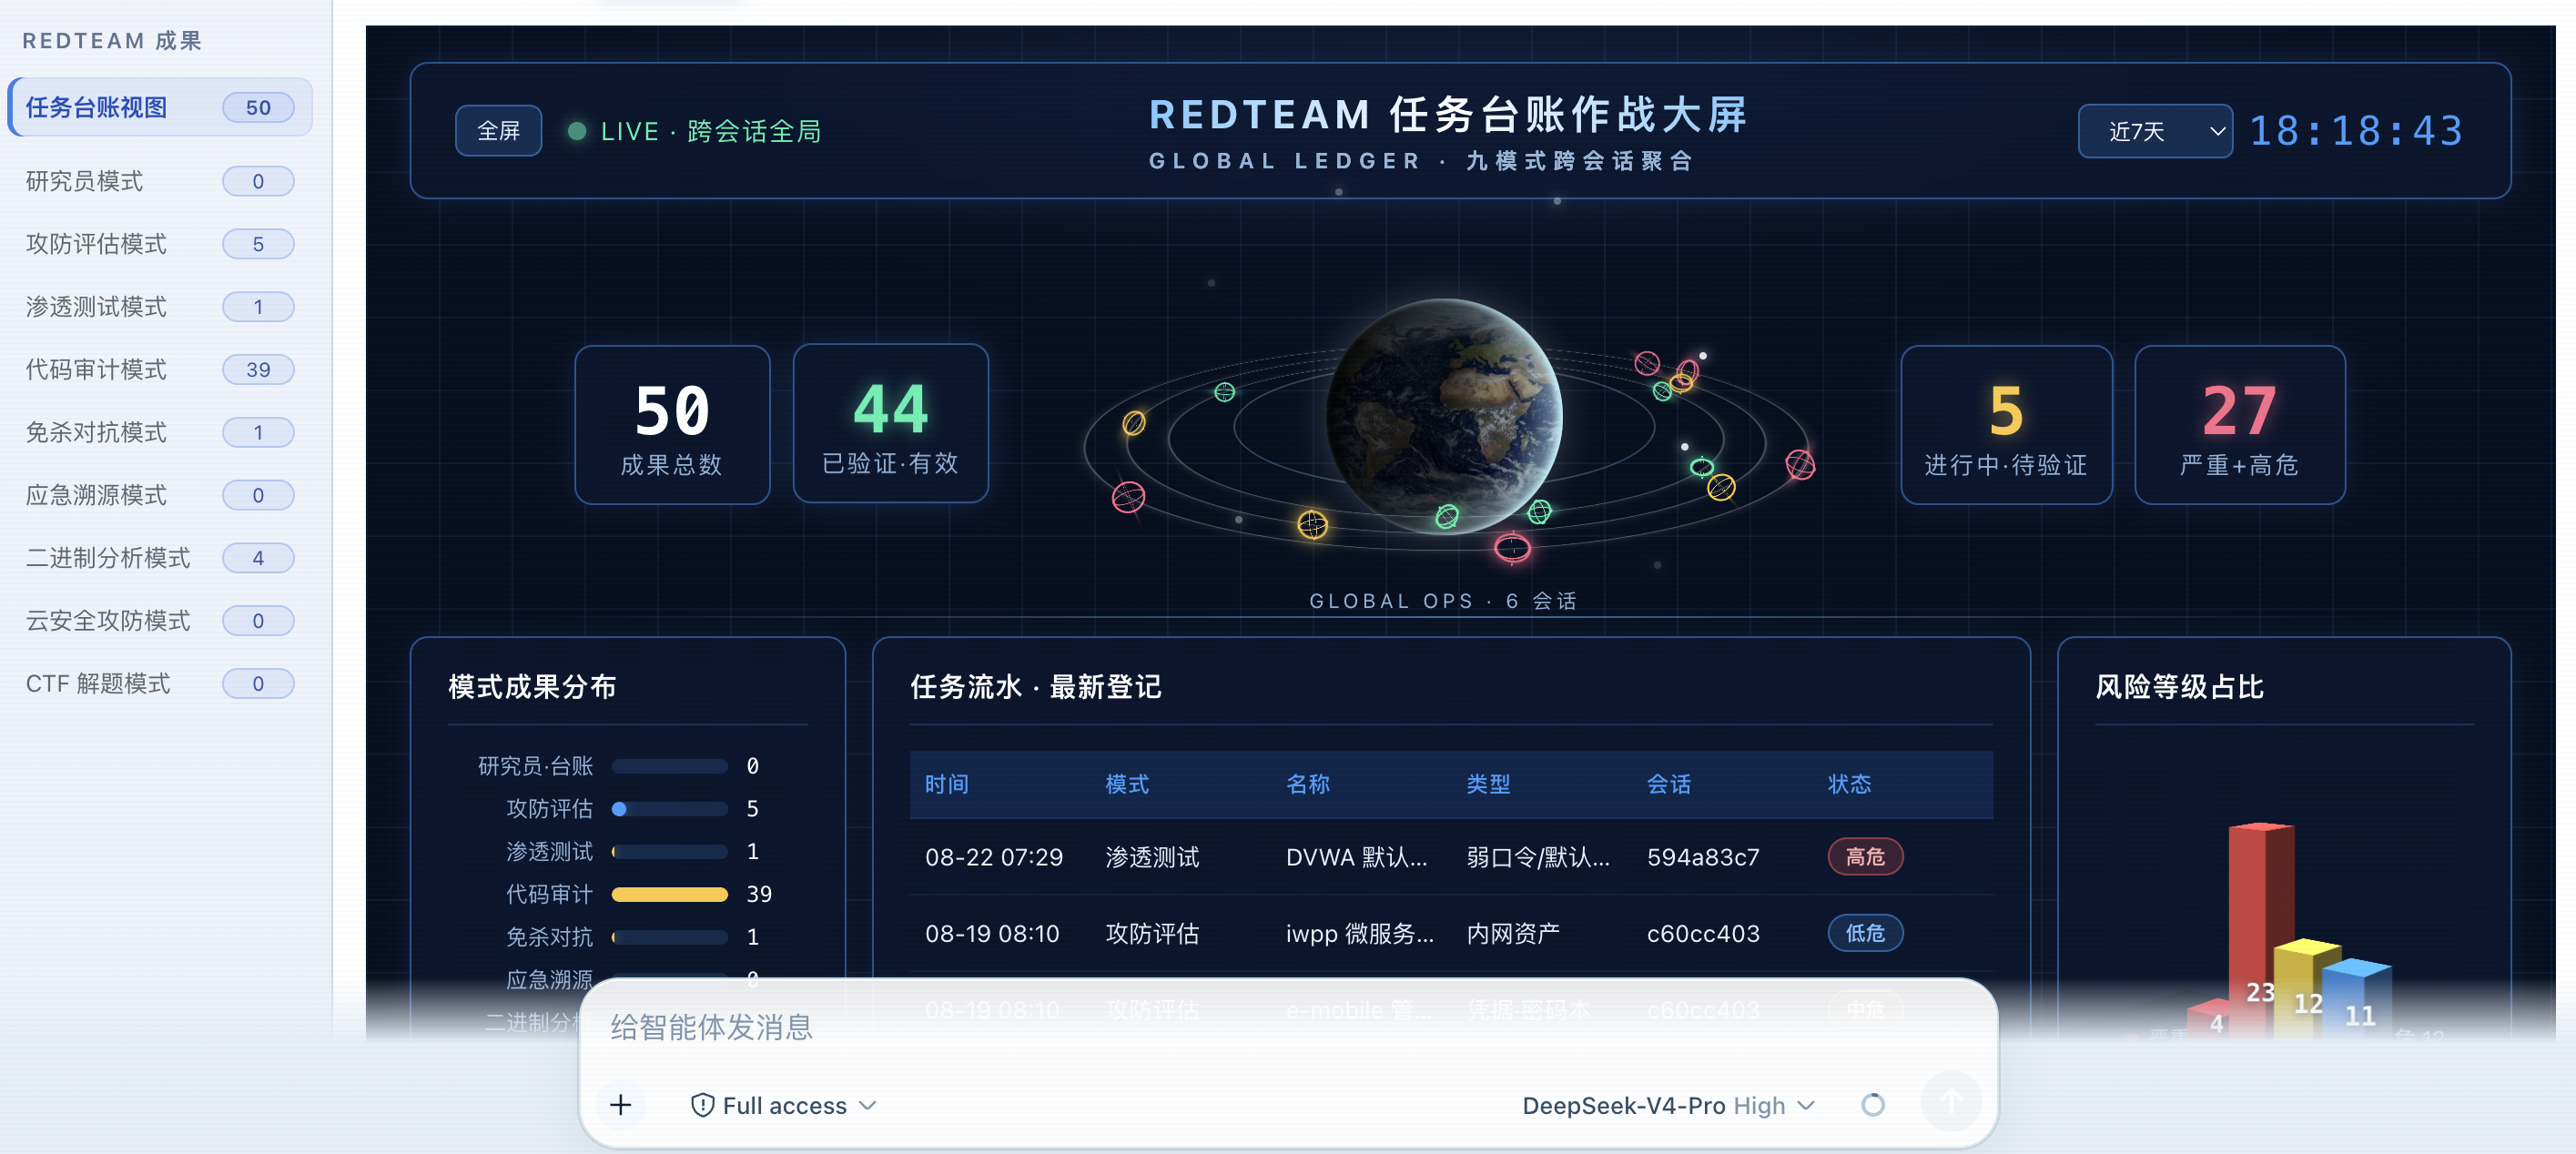 | 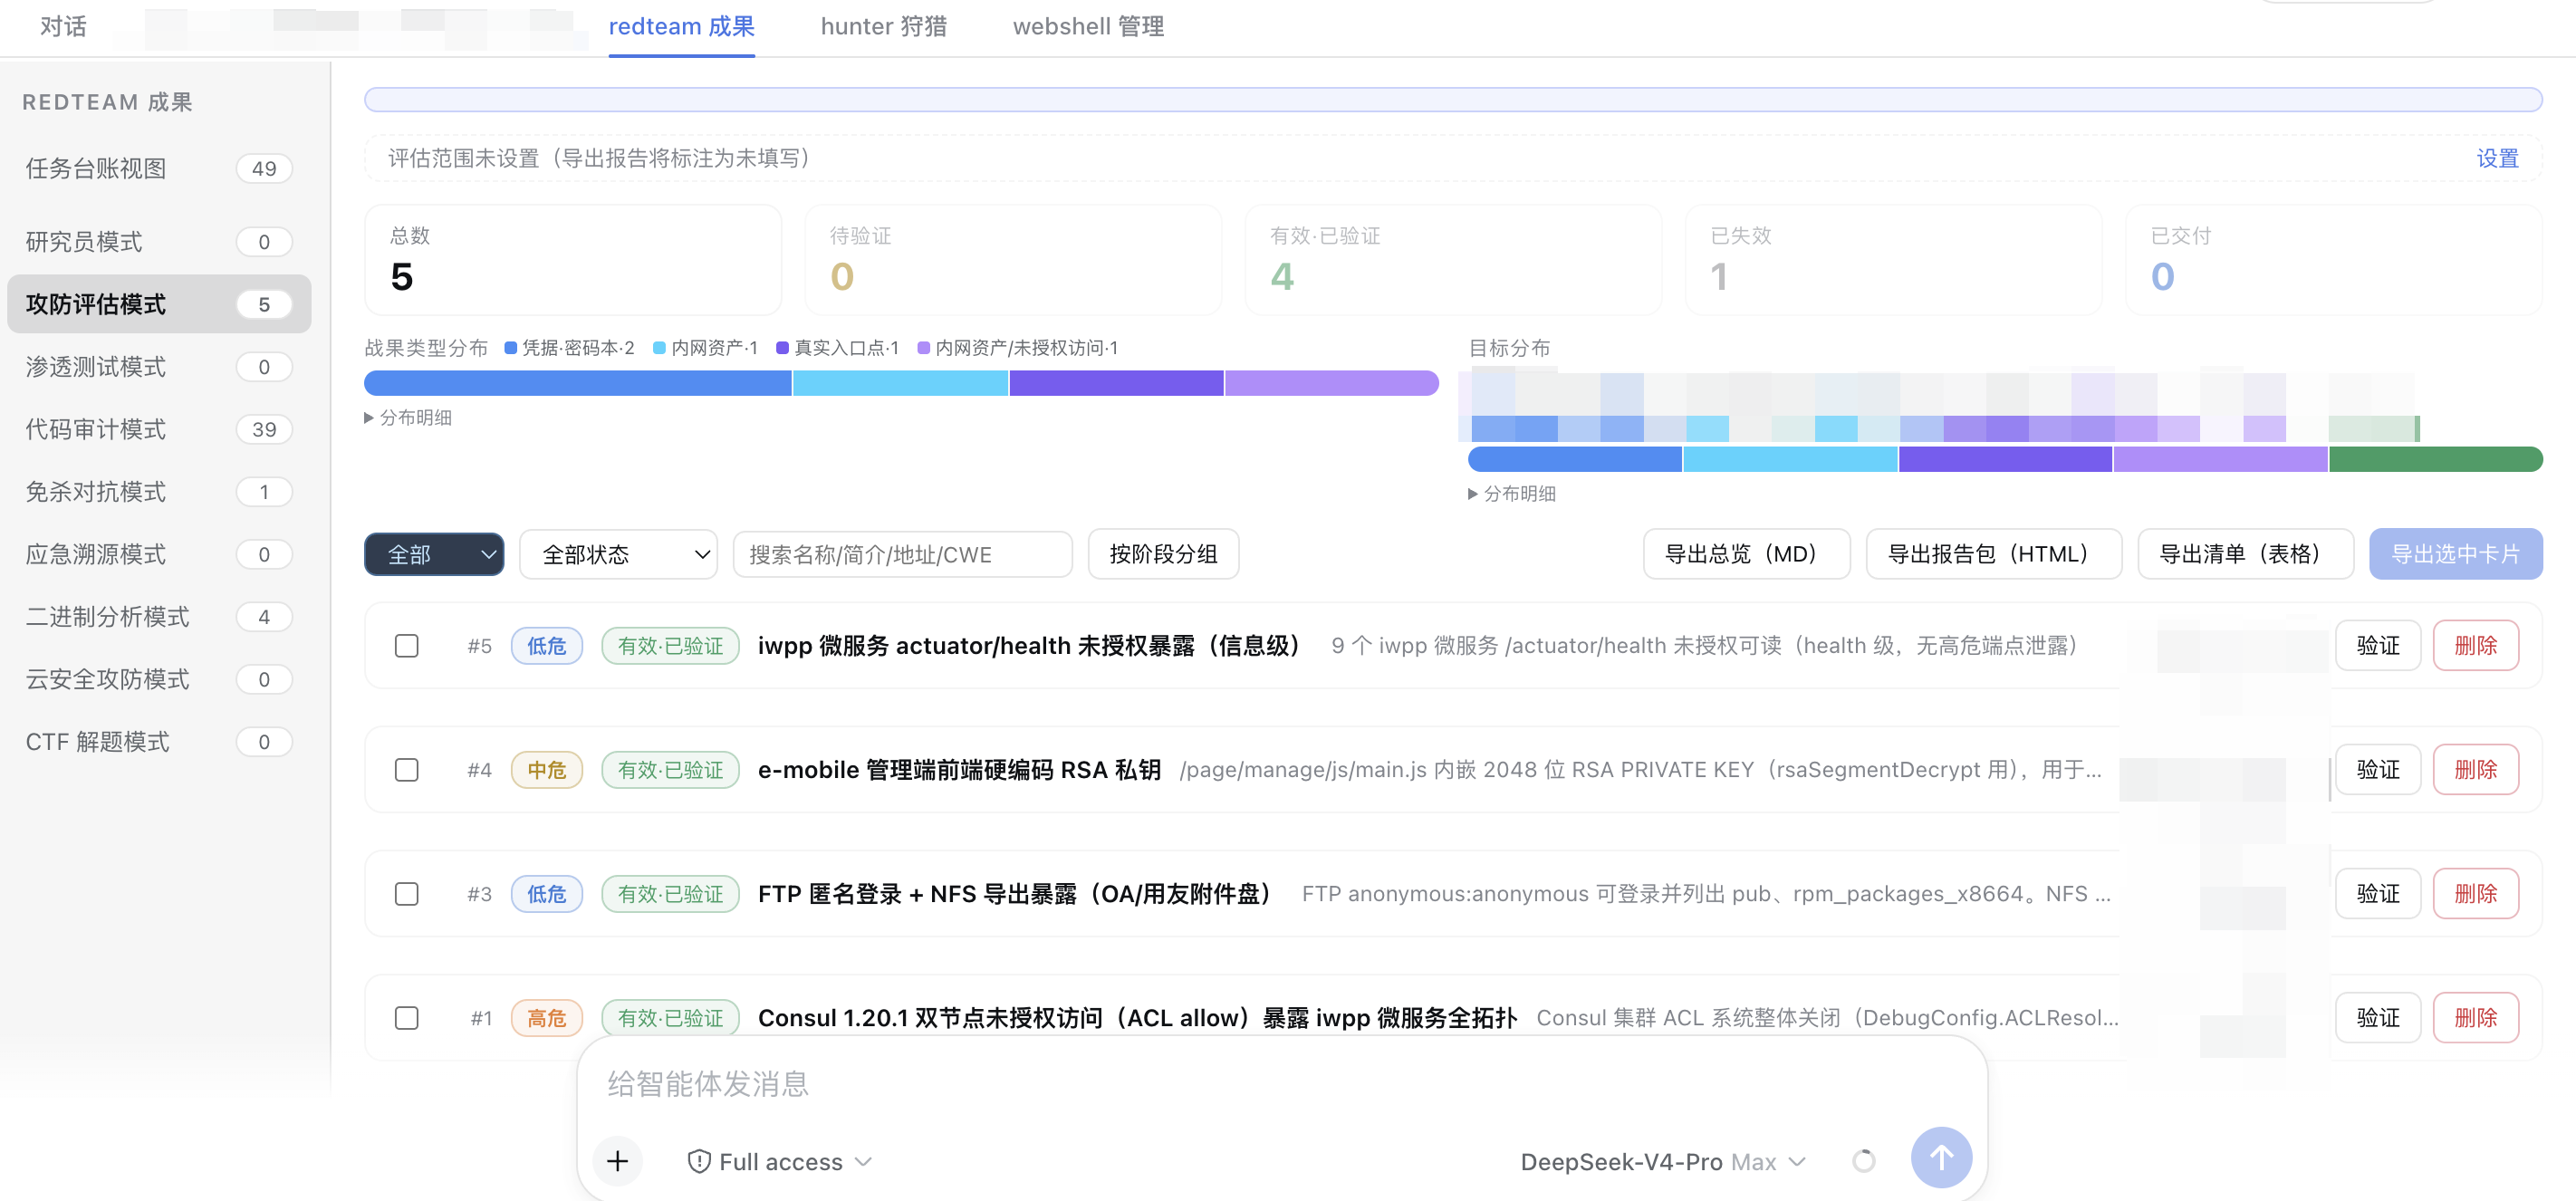 |
| Code Audit Mode (data stats display) | Binary Analysis Mode (data stats display) |
|---|---|
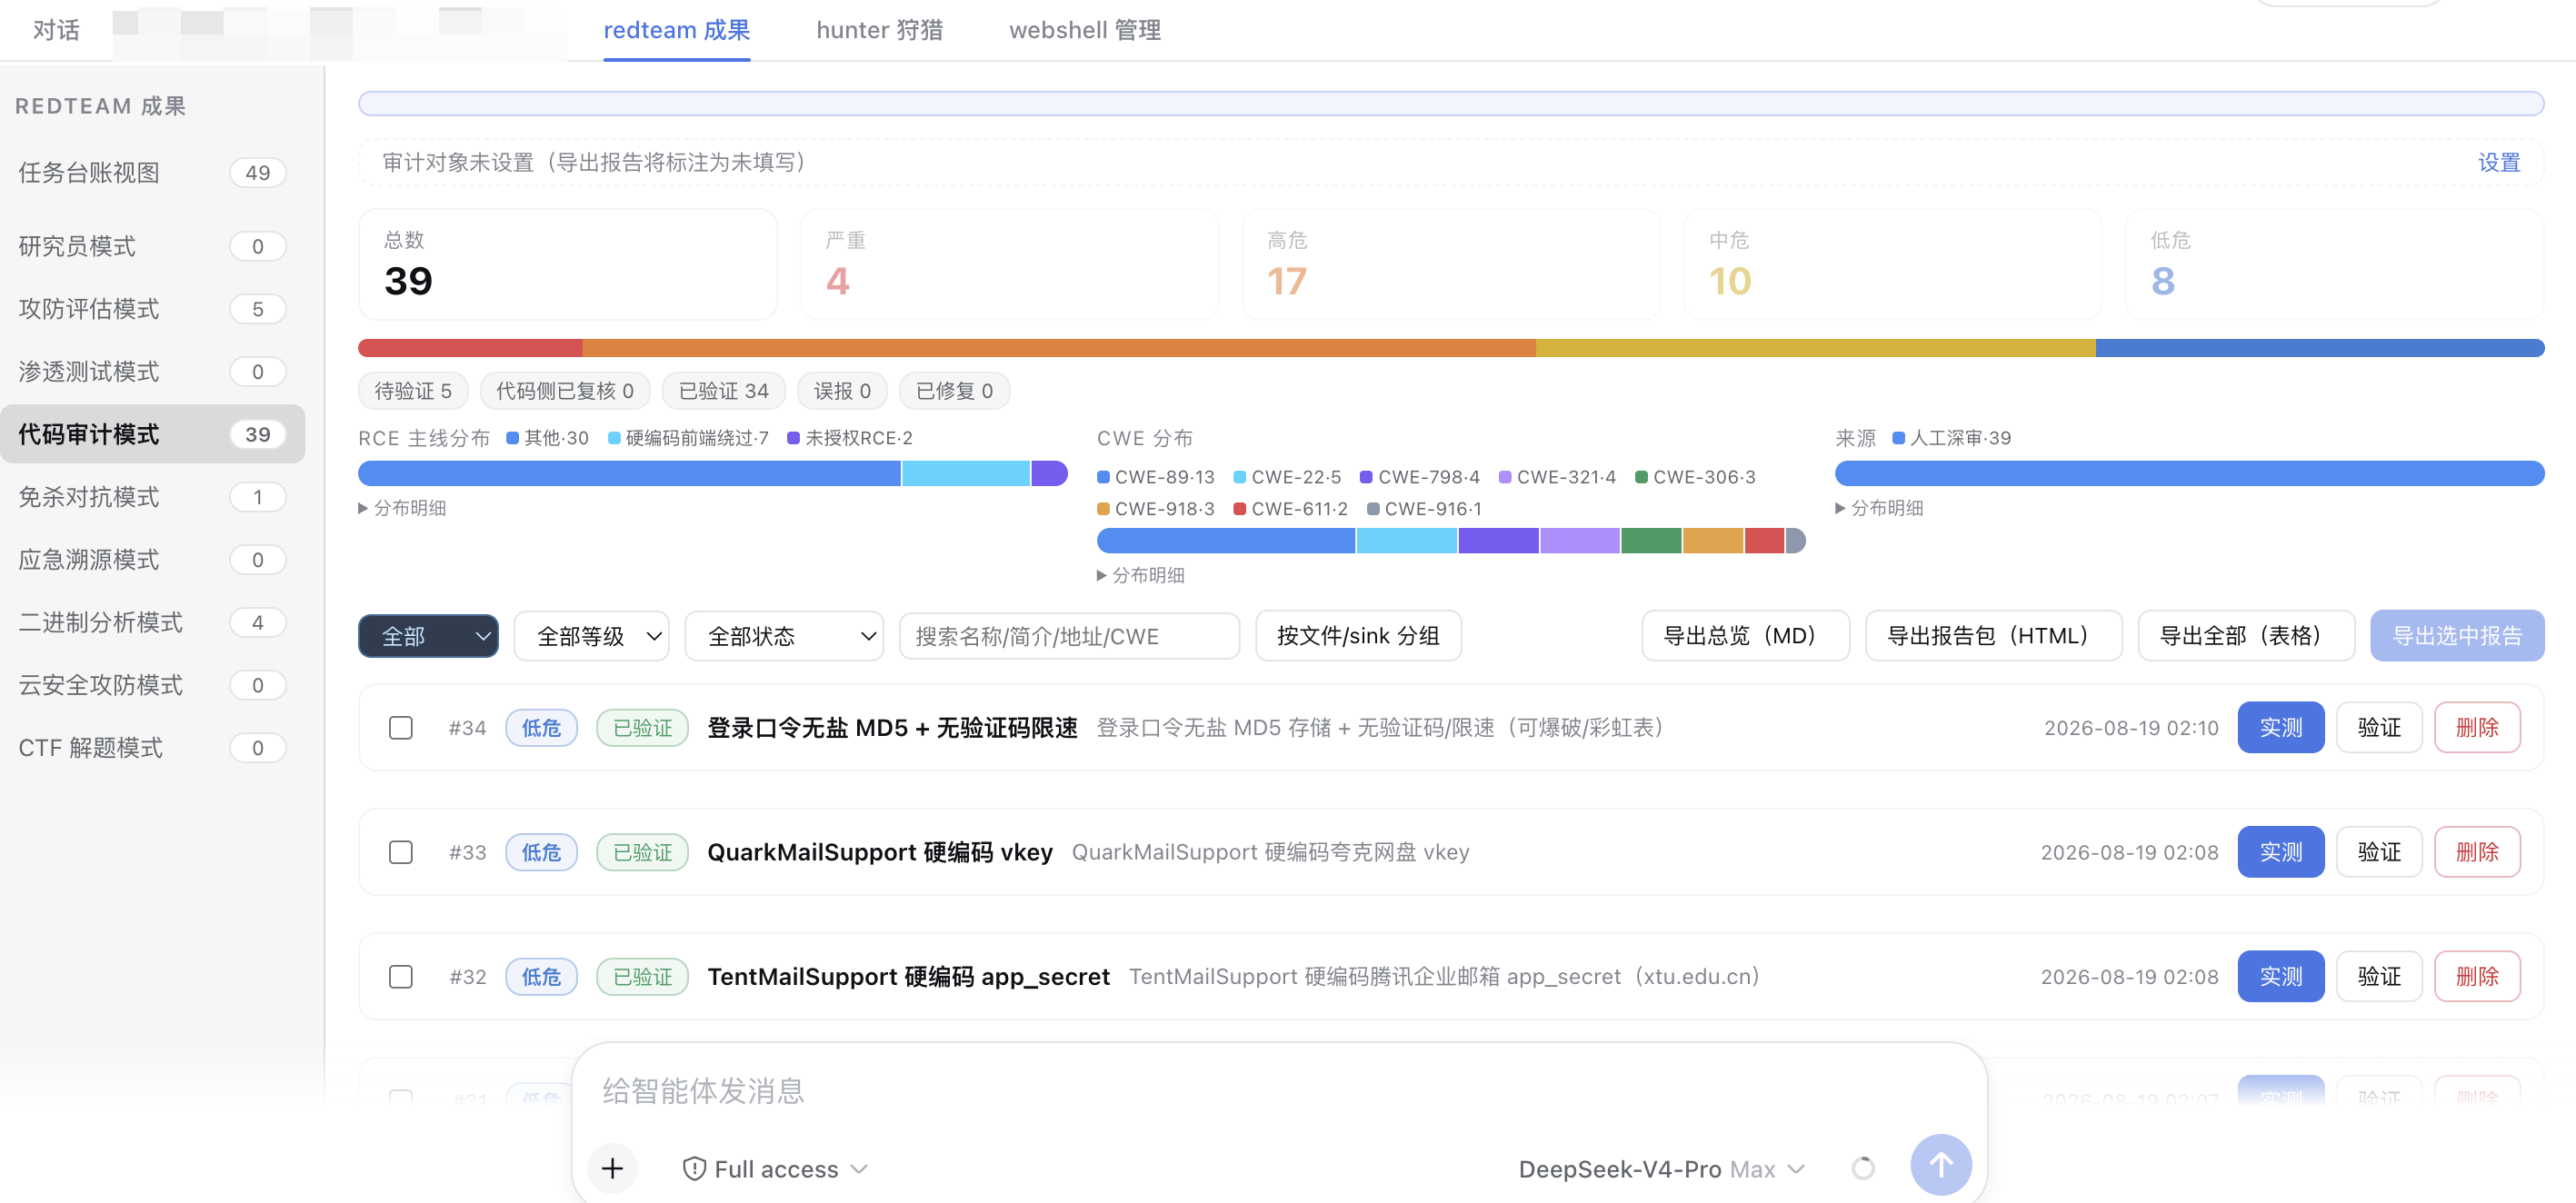 | 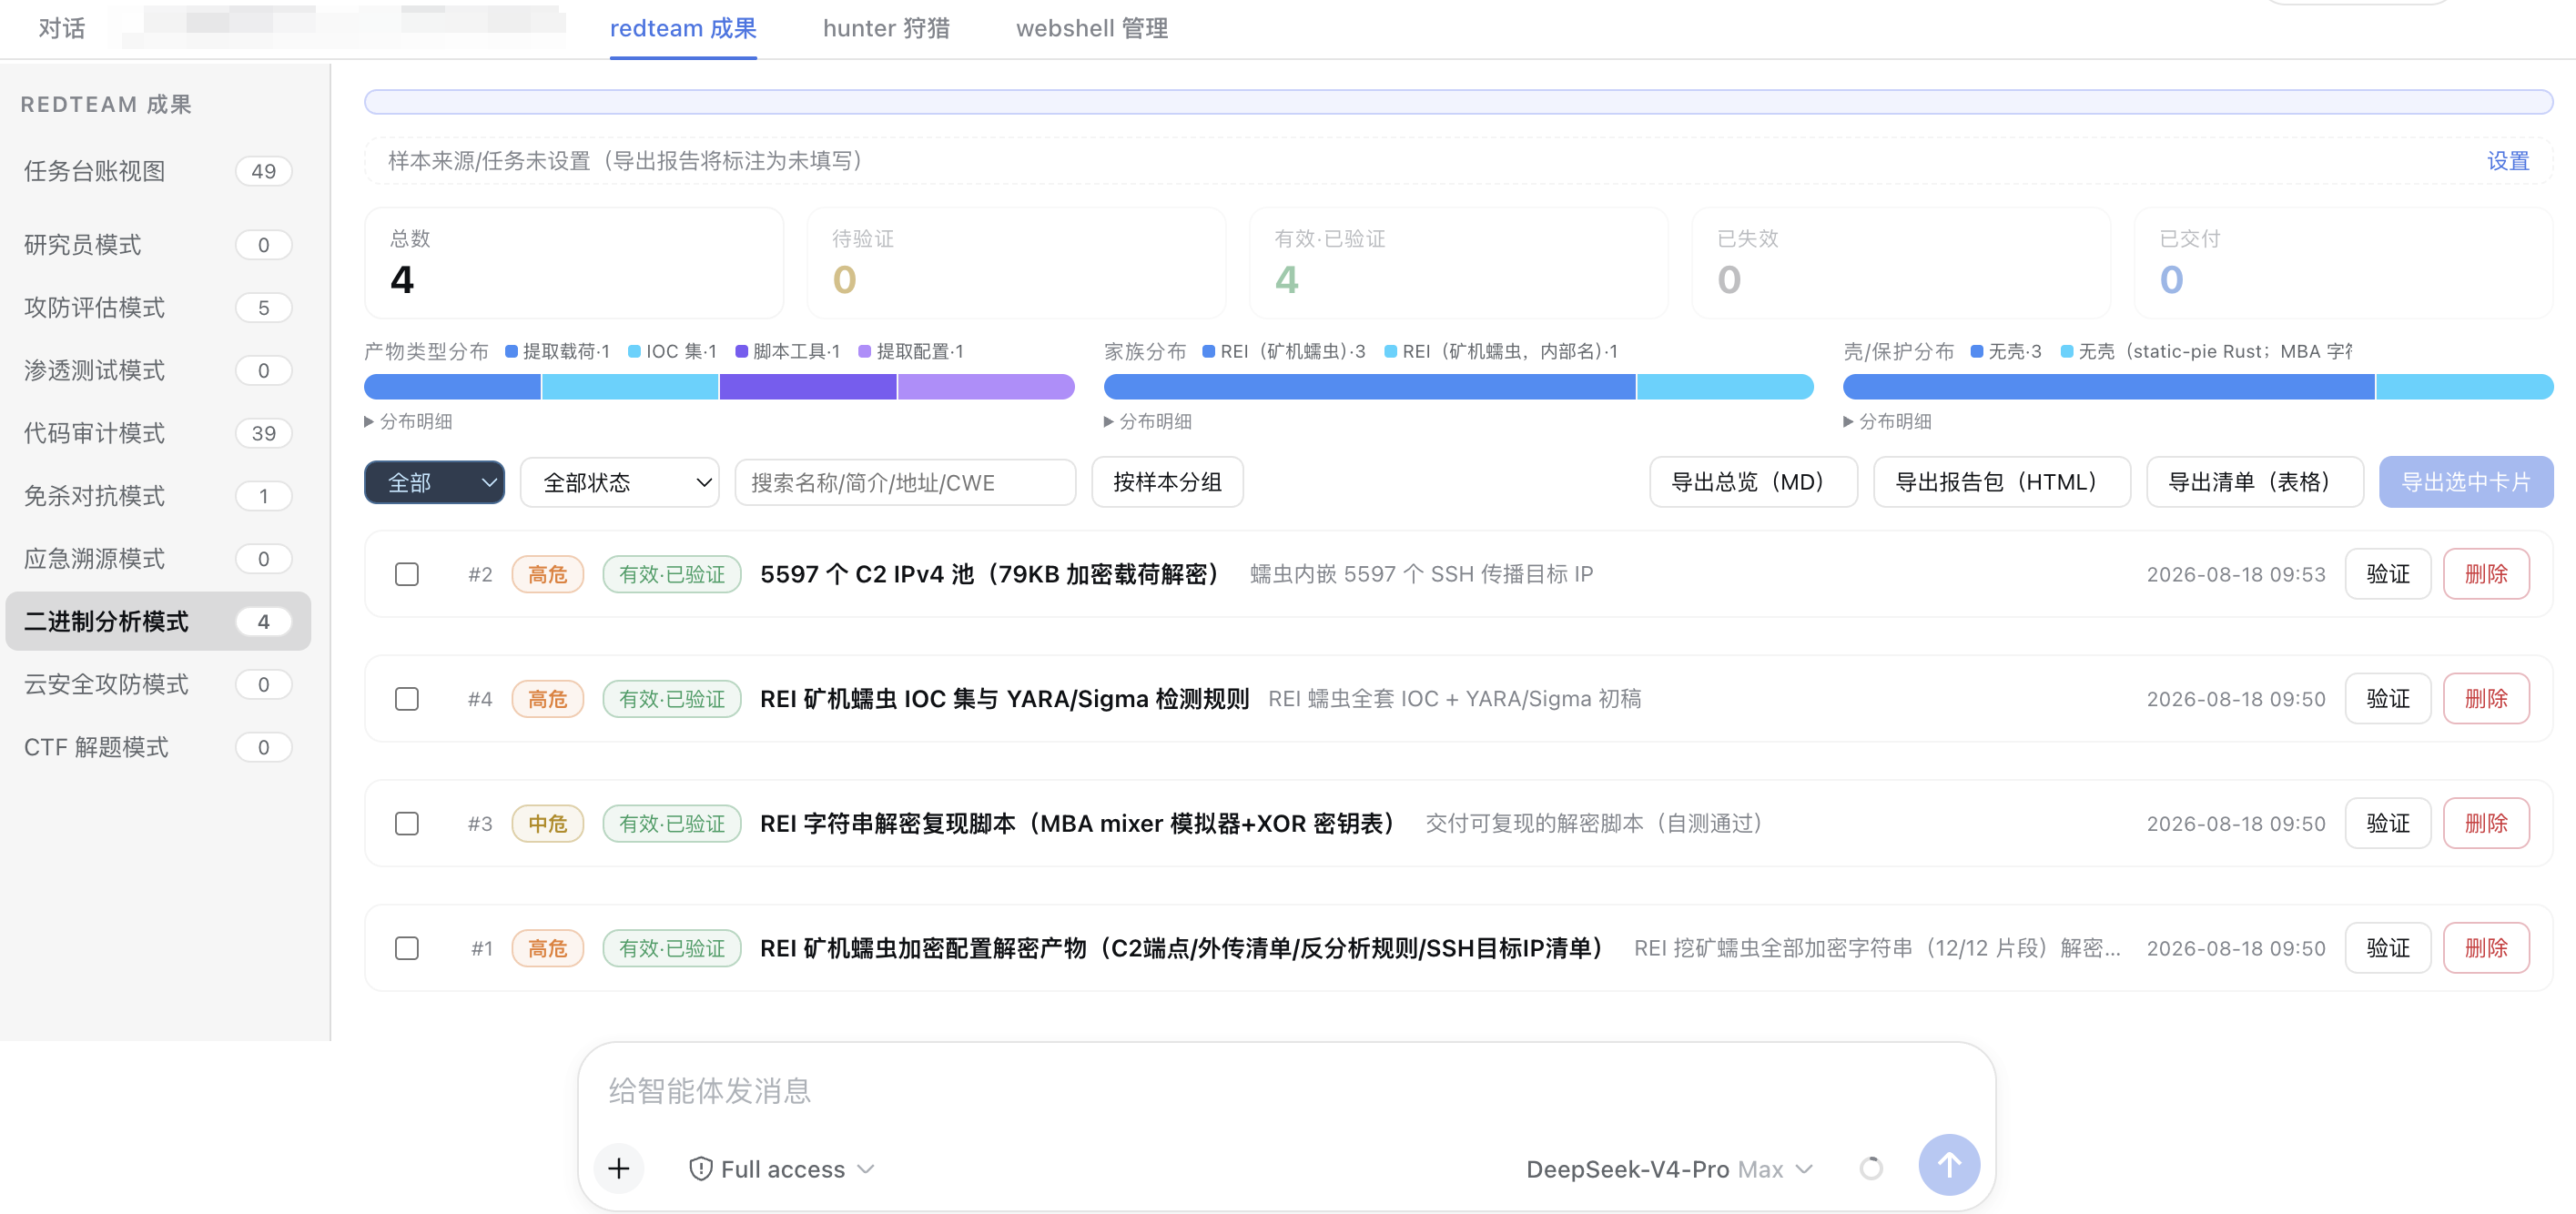 |
| hunter Hunting | webshell Management |
|---|---|
 |  |
| AttackAtlas (Attack Surface Map) |
|---|
 |
Issues
If you encounter bugs, false positives/negatives, or documentation/behavior mismatches during use, please submit to Issues with: mode name, reproduction steps, expected vs. actual behavior, and relevant log snippets (gate-log/enforce-log/session output).
Contributors
Thanks to contributors:
- @yzke —— Settings Page Redteam Manager Console (one-click deploy/install/update/uninstall)
- @SeaOf0 —— Project author & maintainer
Contributions via Pull Request are welcome.
Credits
Thanks to the authors of these projects for the knowledge shared:
- https://github.com/Just-Hack-For-Fun/Linux-INCIDENT-RESPONSE-COOKBOOK
- https://github.com/Just-Hack-For-Fun/Windows-INCIDENT-RESPONSE-COOKBOOK
The asset-mapping mode's full fingerprint database rebuild script (asset-mapping-playbook/scripts/fpdb_update.py) fetches data at runtime from the following open-source fingerprint databases:
- https://github.com/EASY233/Finger
- https://github.com/EdgeSecurityTeam/EHole
- https://github.com/0x727/FingerprintHub
- https://github.com/Mr-xn/Finger
License
Disclaimer
This project is for security research, education, and authorized security testing only (penetration testing authorization letters, CTF, bug bounty programs). Users must:
- Use only with target owner's written authorization;
- Comply with local laws;
- You bear all responsibility for consequences.
The author and contributors shall not be liable for any misuse, nor for any direct or indirect losses. Do not use for illegal activities.
Comments
Loading…
Similar plugins
by chs-1108
DeepSeek Harness 本机安全评测与提示词清洗插件:侧栏面板管理提示词分层、补丁、规则集与技能;带授权演练台。Local security-eval & prompt-cleaning plugin for DeepSeek Harness.
★ 4
MIT
JavaScript
Oct 22, 2026
dsh plugin --profile web add dsh-purgeby SiriLee
Per-edit approval gate for DeepSeek Harness — red/green line diff review before write/edit/stream operations · DSH 插件:逐操作审批门,write/edit/stream 执行前进行红绿行级 diff 审查
★ 4
↓ 346/wk
MIT
TypeScript
Sep 28, 2026
dsh plugin --profile web add dsh-edit-approvalby shaoshi20
Security scanner for DSH plugins: static and semantic passes over plugin source, DSH-specific attack-surface rules, npm audit, batch scanning, and an HTML report with per-finding severity and evidence
★ 11
↓ 234/wk
MIT
TypeScript
Oct 9, 2026
dsh plugin --profile agent add @shaoshi/dshscanby jkrandom-sudo
Security audit for DeepSeek Harness plugins: static permission profile with file/line evidence + a runtime sentinel gating credential access and unknown-host egress · DSH 插件安全审计:静态权限画像(附文件/行号证据)+ 运行时哨
★ 4
↓ 85/wk
MIT
TypeScript
Sep 11, 2026
dsh plugin --profile web add dsh-plugin-auditby 9931666
Crossfire (针锋) for DeepSeek Harness: put a settled result on the stand, let red-team experts attack it from chosen dimensions, and adjudicate every single defect yourself. The machine only finds flaws; the human always owns the verdict.
★ 1
TypeScript
Oct 25, 2026
dsh plugin --profile web add @y9931666/dsh-plugin-crossfireStatic and runtime security guard for dsh: rule-based scans for malicious code, prompt injection and token waste, runtime interception of dangerous tool calls, /scan command, plugin_scan tool, web pan
★ 0
dsh plugin --profile web add dsh-security-guard