

dsh-pentest
Manifest valid★ 611Penetration Testing Mode for DeepSeek Harness (dsh) @CloverSecLabs
dsh-pentest — DSH Penetration Testing Mode
A penetration testing mode for DeepSeek Harness (dsh): Within the scope of authorization, it records targets, explores clues, validates results, manages assets and vulnerabilities, and presents them in a Web UI with exploration chain, vulnerability, and asset views.
This directory is a self-contained bundle package (@howmp/dsh-pentest): the host plugin, Web UI, and sqlite backend are all shipped together via the package's exports.
Release assets can be installed directly with dsh plugin add.
Installation
Install from a Release URL
dsh plugin --profile web add https://github.com/howmp/dsh-pentest/releases/latest/download/dsh-pentest.tar.gz
Or install from local file
dsh plugin --profile web add file:C:\path\to\dsh-pentest.tar.gz
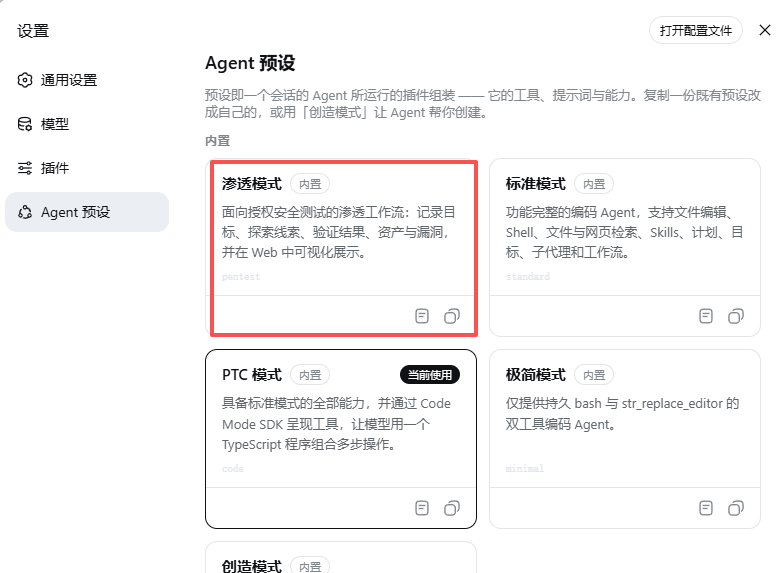
After restarting dsh, pick the auto-registered "Pentest Mode" in the new session.
UI Preview
Mode Selection
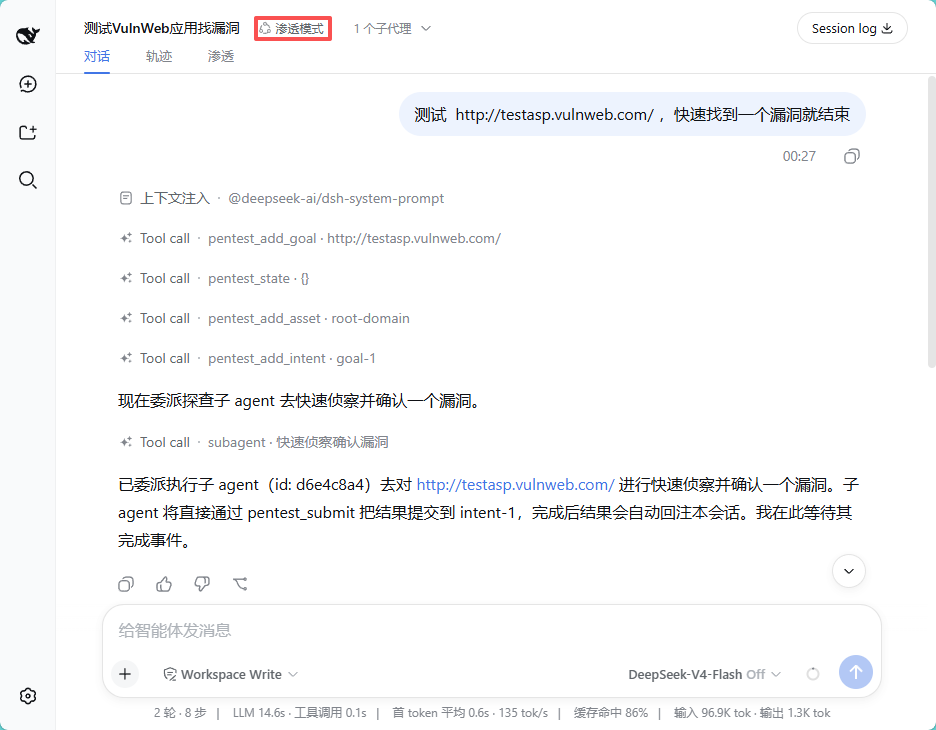
Chat & Execution
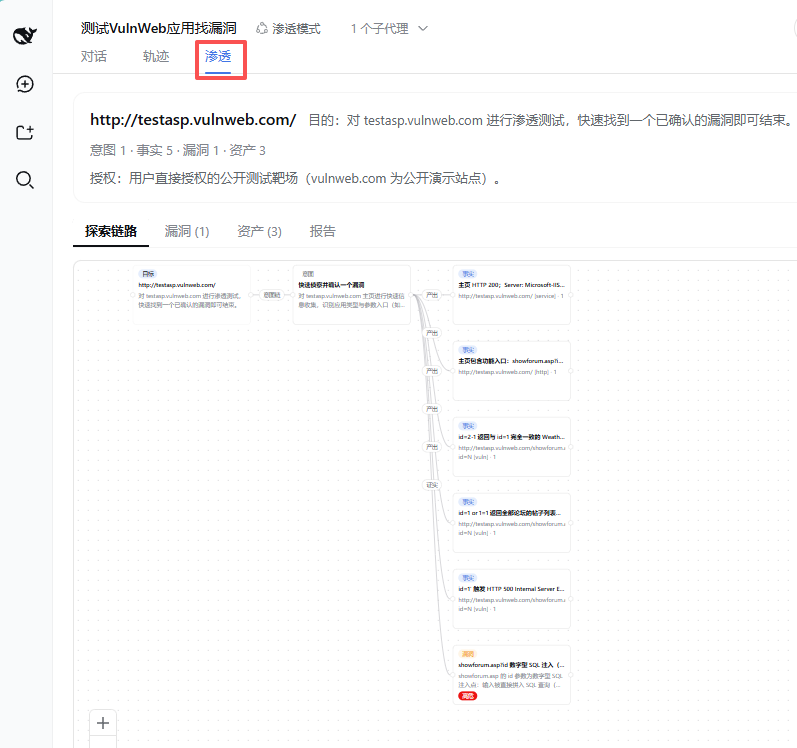
Exploration Chain
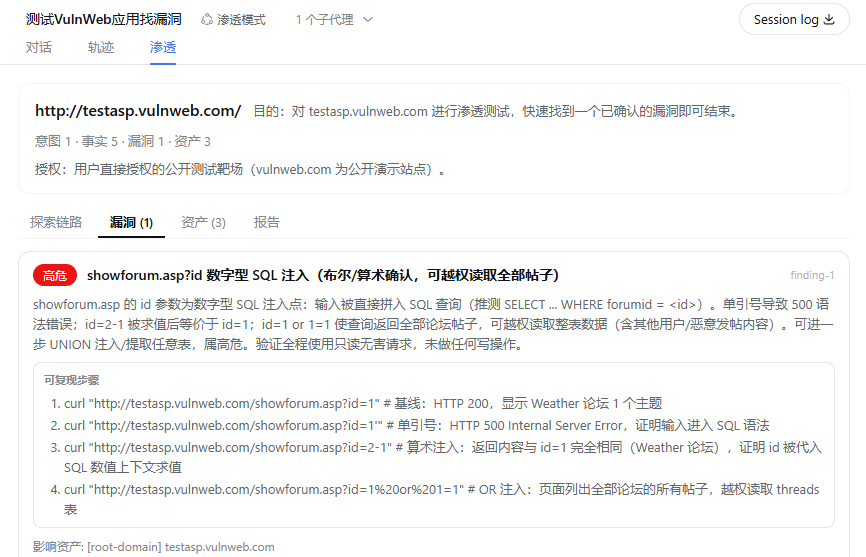
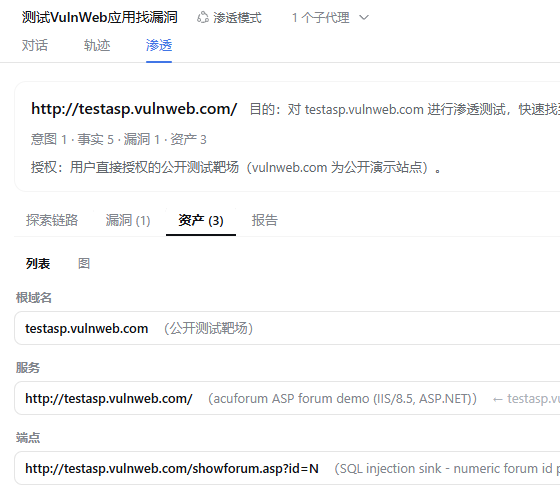
Vulnerability View
Asset View
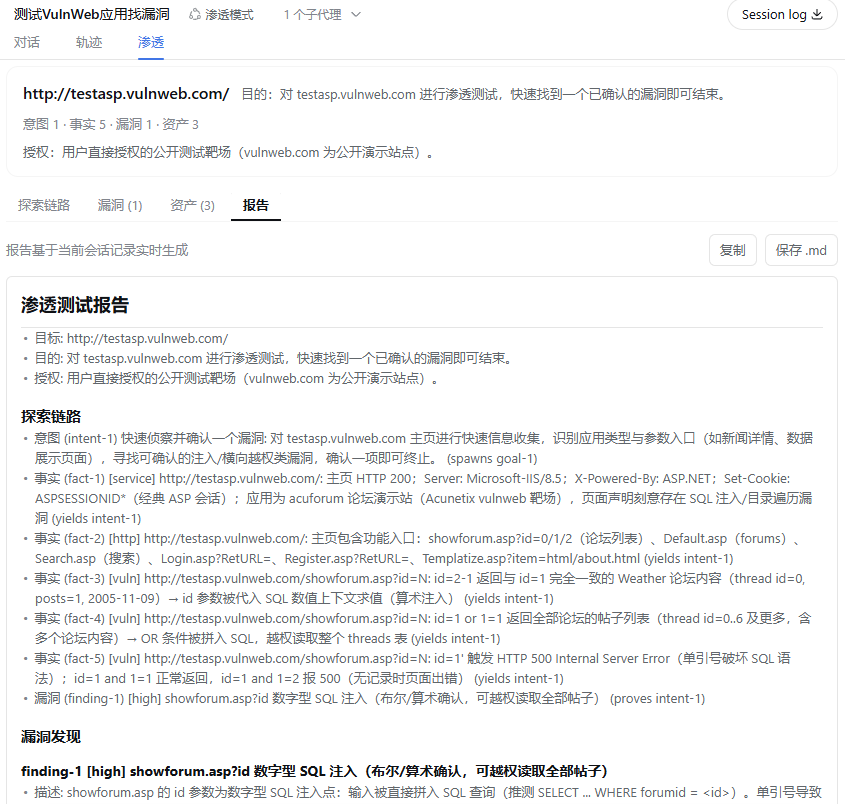
Test Report
Architecture
- Domain model (
src/dsh-pentest/src/spec.ts): storage domainpentest(version 2) — six tables:goals/intents/facts/findings/assets/edges. Edges form the chain vocabulary:spawns(goal→intent),yields(intent→fact),derived_from(fact→intent),proves(intent→finding); asset relationships useparent(asset→asset). Findings requirereproducibleSteps(at least one). - Deterministic ids (
store.ts): node/edge ids are<kind>-<n>(counted per session, reset to zero after a goal reset) — tools return ids for the model to reference across calls, and the session projection replays the same graph purely from logs. - Tools (
tools.ts):pentest_submit(sub-agent writes directly to a designated parent intent) /pentest_add_goal(resets the entire graph) /pentest_add_intent(exactly one anchor) /pentest_add_fact/pentest_add_finding(steps required, can link to affected assets) /pentest_add_asset(optional parentId, empty string treated as root asset) /pentest_state/pentest_graph/pentest_report. - Session projection (
projection.ts): folds loggedpentest_*calls into{ goal, nodes, assets, edges, counts }, mirroring the store's reference rejection; cap of 200 each. Also registers a per-sessionpentestMountedmarker unit: set to true when the session's own logs prove that this plugin was composed/ mounted (request headers assemblepentest_*tools / logged calls / sub-agent delegated submissions), for Web tab determination. - Web tabs (
src/dsh-client-ui-pentest): registered per session (shown when the current session or its ancestor chain in the list matches thepentestpreset name, apentest-*copied preset name, or the session carries thepentestMountedmarker; sessions without evidence are hidden); four sub-tabs — Exploration Chain (@xyflow/react graph, edges carry relation pills: intent chain / yields / derived from / proves), Vulnerabilities (severity / description / reproducible steps / affected assets), Assets (list / graph two modes), Report (Markdown rendering, copy and save). - Protocol (
instructions.ts): system prompt sectionpentest:protocol(order 50), progressing along the chain, sub-agents write directly to parent intent viapentest_submit, assets parent-before-child, all user interactions in Chinese.
Known Limitations
- Database: penetration records are written to
$DSH_HOME/storages/pentest-sessions.db(sqlite, routed via bundle patch). Storage for other host domains is unaffected (still the host's default json backend). - Authorization: only test targets that are authorized. The
authorizationparameter ofpentest_add_goalcan include authorization details (authorized party / written permission reference), which is recorded in state and the final report for audit; it is merely an audit fact, not a gate — scanning/exploitation actions are still subject to deployment sandbox and approval constraints. - Records are scoped to a single session; no cross-session/project continuation; starting a new engagement requires a fresh
pentest_add_goal. - Derived presets: presets do not support inheritance; simply copy the entire
preset/pentest/directory following the official approach and modify as needed (tools, protocol, projection all take effect accordingly). Web tab detection is decoupled from preset names: keeping thepentest-prefix when copying (e.g.,pentest-sec) shows it immediately; renaming a copied preset to an arbitrary name will be shown bypentestMounted(session's own log evidence) after the first request in that session — the preset name is not a capability; session logs are. - Web graph is a windowed view: session projections each retain the latest 200 nodes/assets/edges (beyond which the oldest are evicted, and dangling edges are cleaned up synchronously).
UI counts and the graph reflect that window; complete records are authoritative via
pentest_state/pentest_report(reads from the storage layer). - Graph layout is static hierarchical (pannable and zoomable, nodes not draggable).
- Runtime requirement: the sqlite backend uses Node.js
node:sqlite; the host runtime requires Node.js >= 22.5.
Layout
dsh-pentest/                   # 项目根 = bundle 包 @howmp/dsh-pentest(自带 zod/schemastery 运行时依赖,其余宿主提供)
├── package.json               # bundle manifest:dsh.bundle.patch + dsh.client + exports 子路径
├── cordis.patch.yml           # 补丁层:UI、sqlite 后端与 storage-domain 路由
├── lib/                       # 构建产物(npm pack 的内容)
│   ├── index.js               #   包入口:空 apply
│   ├── pentest.js             #   宿主渗透插件:9 个 pentest_* 工具 + 协议注入 + 会话投影/挂载标记
│   ├── preset-root.js          #   注册包内只读「渗透模式」预设目录(兼容 DSH rc.6)
│   ├── storage-sqlite.js      #   渗透记录专用的 sqlite 后端(node:sqlite)
│   ├── ui-pentest.js          #   Web 插件宿主半:空 apply(0.1.1 时代的子路径行座位;bundle 已改挂包根)
│   ├── ui-pentest.client.js   #   Web 插件浏览器半:渗透视图标签页(4 个子标签,@xyflow/react 内联)
│   └── invariant.js           #   探索图不变量伴生(与官方各包同构,生产环境不加载)
├── src/                       # 源码快照(继续开发/重新构建用)
│   ├── index.ts / invariant.ts
│   ├── dsh-pentest/               # host 包源码:src/ + tests/ + tsconfig + tsdown + README
│   └── dsh-client-ui-pentest/     # client 包源码:src/client/(视图/图布局/注册)+ tests/
├── tests/bundle.spec.ts       # bundle 补丁层测试
├── packages/                  # 三个构建好的子包(仅作构建源保留;bundle 不再依赖它们)
│   ├── dsh-pentest/               # host 插件源码构建产物
│   ├── dsh-client-ui-pentest/     # Web 界面插件源码构建产物
│   └── dsh-storage-sqlite/        # sqlite 后端构建产物(来自 dsh 仓库,无独立源码)
├── preset/pentest/            # 「渗透模式」agent 预设(由 bundle 自动注册)
├── images/                    # README 界面预览截图
└── README.md
Reference Projects
Compatibility
Versions
| Latest version | Published | Size |
|---|---|---|
| 0.0.0-stage | — | — |
| 0.1.0-rc.35 | — | — |
| 0.1.0-rc.36 | — | — |
| 0.1.0-rc.37 | — | — |
Comments
Loading…
Similar plugins
by truelove-dreamer
DeepSeek Harness plugin: heuristic malware vetting for installed third-party plugins
★ 4
↓ 174/wk
JavaScript
Aug 26, 2026
dsh plugin --profile web add dsh-plugin-vettingby fu827707013
DSH(DeepSeek Harness)并发请求监控与门闩插件。
★ 4
↓ 177/wk
MIT
JavaScript
Sep 17, 2026
dsh plugin --profile web add dsh-concurrency-guardby R1145141919810
VulnClaw penetration-testing mode for the DeepSeek Harness: nmap, HTTP probing, directory/JS recon, traffic evidence, reports and PoCs as native Harness tools. Based on VulnClaw (MIT) by UncleC.
★ 1
MIT
JavaScript
Oct 15, 2026
dsh plugin --profile web add @local/dsh-vulnclaw-pentestby xiangnan0811
DeepSeek Harness plugin for ClinePass: models, API key, and usage limits.
★ 0
MIT
JavaScript
Oct 19, 2026
dsh plugin --profile web add dsh-clinepassby Sutera-Diffusus
DSH sandbox tester: process-isolated testing ground for DeepSeek Harness
★ 5
↓ 2/wk
MIT
JavaScript
Aug 16, 2026
dsh plugin --profile web add dsh-sandbox